AWS Nitro Sandboxes on EKS: Hardware-Isolated Pods Without Leaving Kubernetes
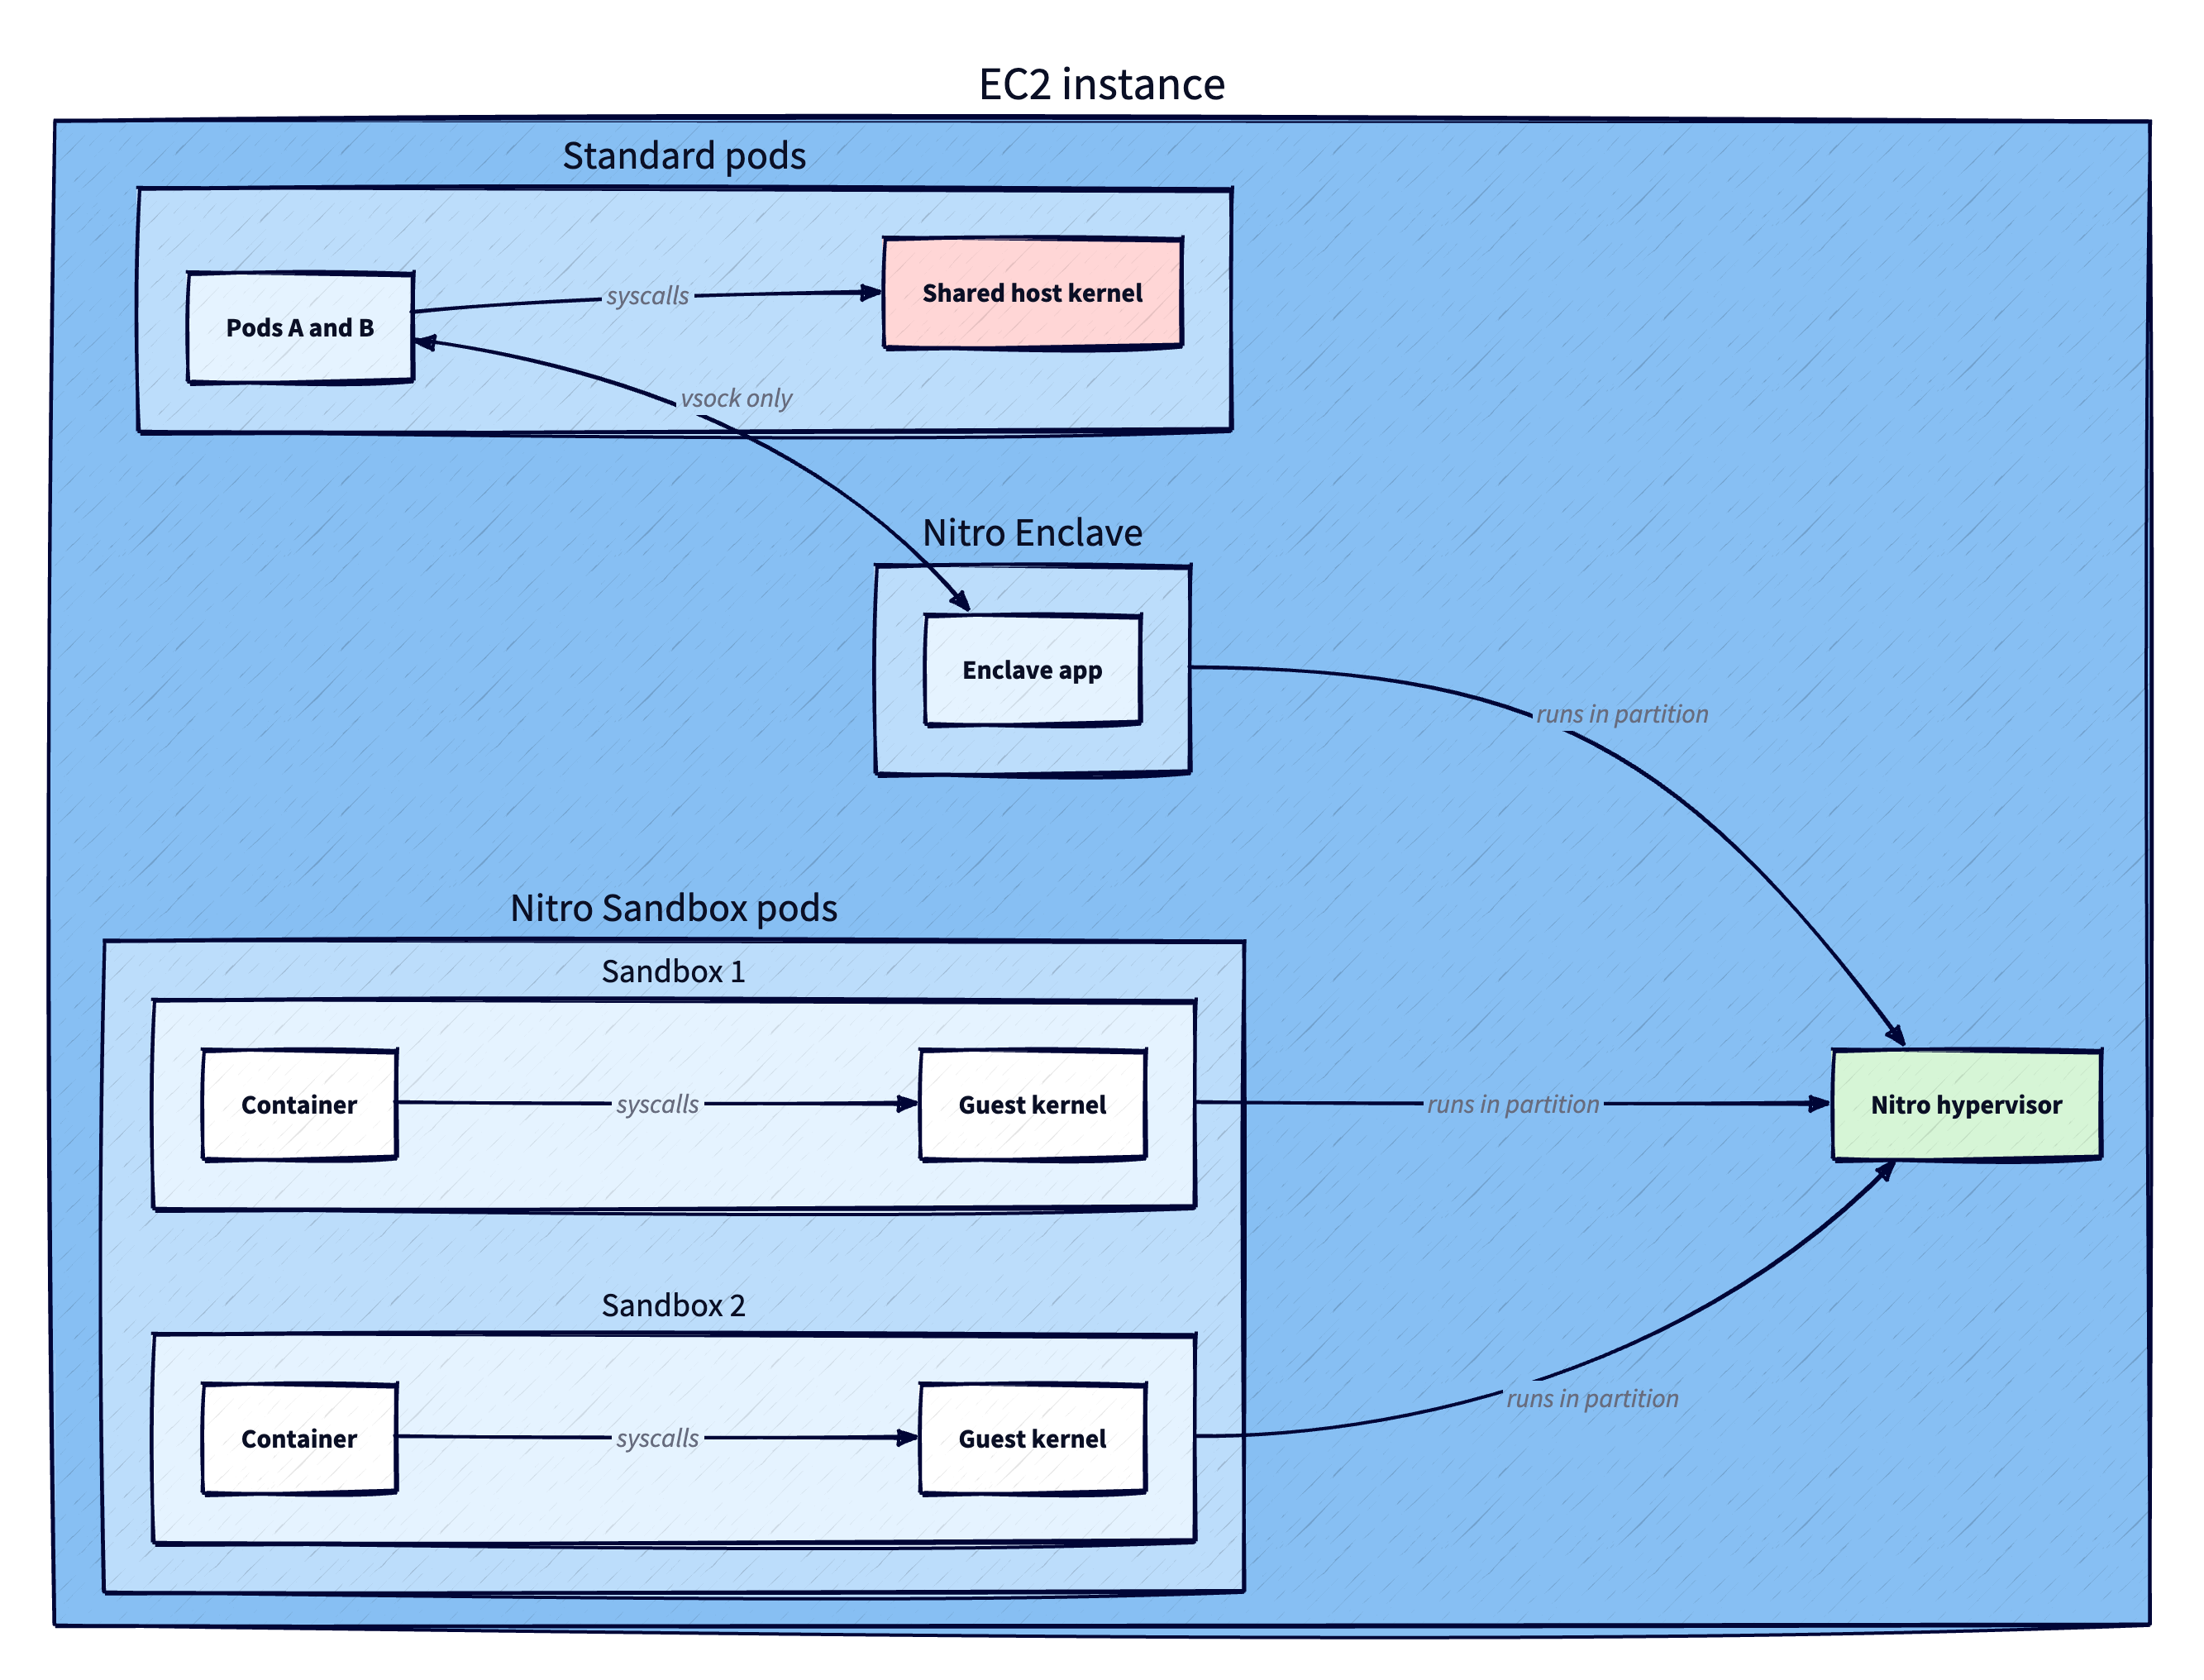
AWS Nitro Sandboxes bring hardware-enforced isolation to individual pods on Amazon EKS. Here is how they differ from standard pods and Nitro Enclaves, how to enable them step by step, and how their security trade-offs compare with Nitro Enclaves and Kata Containers.
If you run regulated or multi-tenant workloads on Amazon EKS, you've probably made peace with an uncomfortable fact: every pod on a node trusts the same Linux kernel. AWS Nitro Sandboxes give individual pods a hardware-enforced boundary while they stay ordinary Kubernetes pods, and you can turn them on with Terraform and one field in the pod spec. Whether that's worth doing depends on where the boundary sits, how it compares with standard pods, Nitro Enclaves and Kata Containers, and which of your workloads justify it.
Read the full article on LearnXops (free with a LearnXops account).