Production-Grade Secrets Management Using HashiCorp Vault
60 Days DevOps Challenge: Day 54
By Sandip Das · · 14 min read
💡
Hey — It's Sandip Das 👋
We must master Vault to securely store, access, and rotate secrets, credentials, and tokens in dynamic environments.
It enables centralized, audit-ready secret management across cloud, Kubernetes, and CI/CD pipelines, reducing risk and ensuring compliance.
We must master Vault to securely store, access, and rotate secrets, credentials, and tokens in dynamic environments.
It enables centralized, audit-ready secret management across cloud, Kubernetes, and CI/CD pipelines, reducing risk and ensuring compliance.
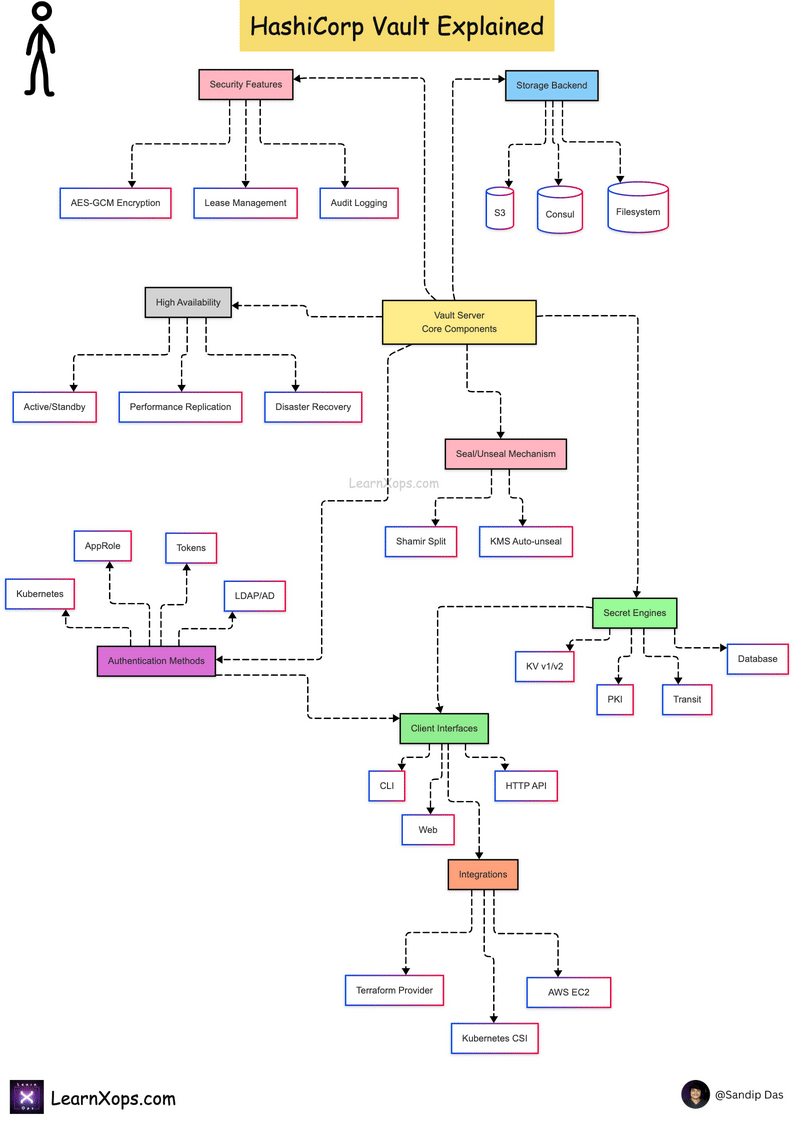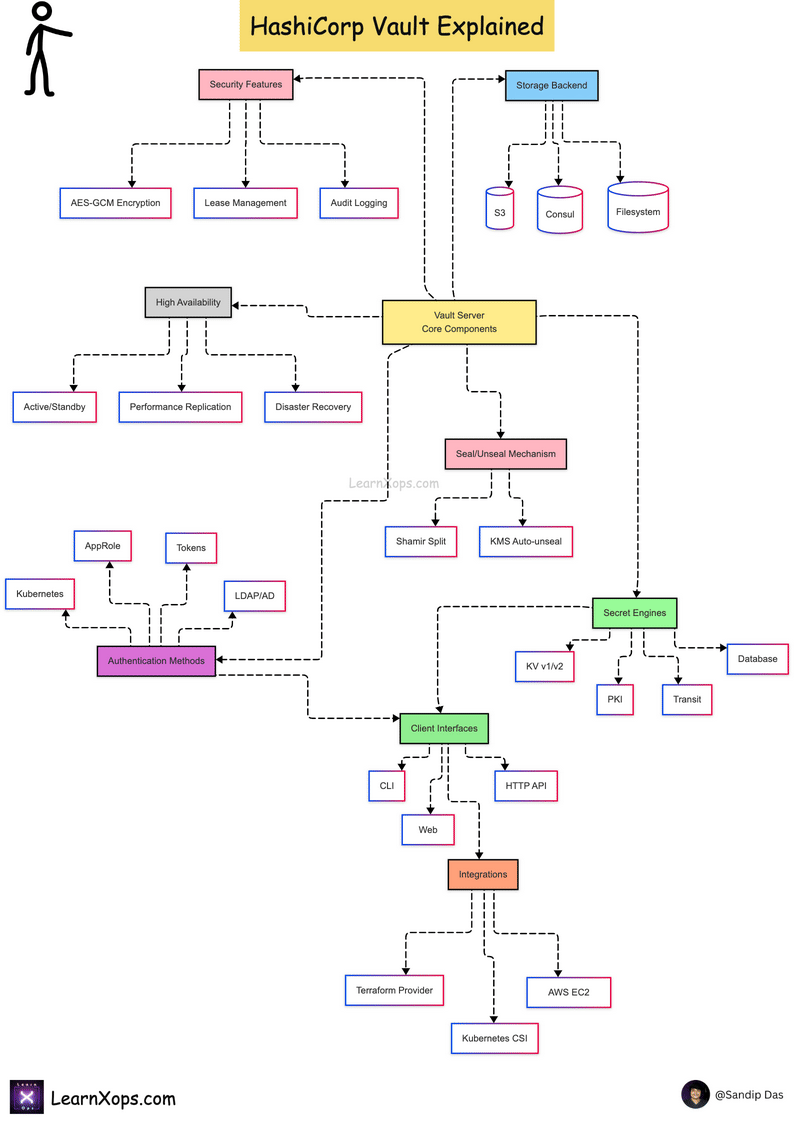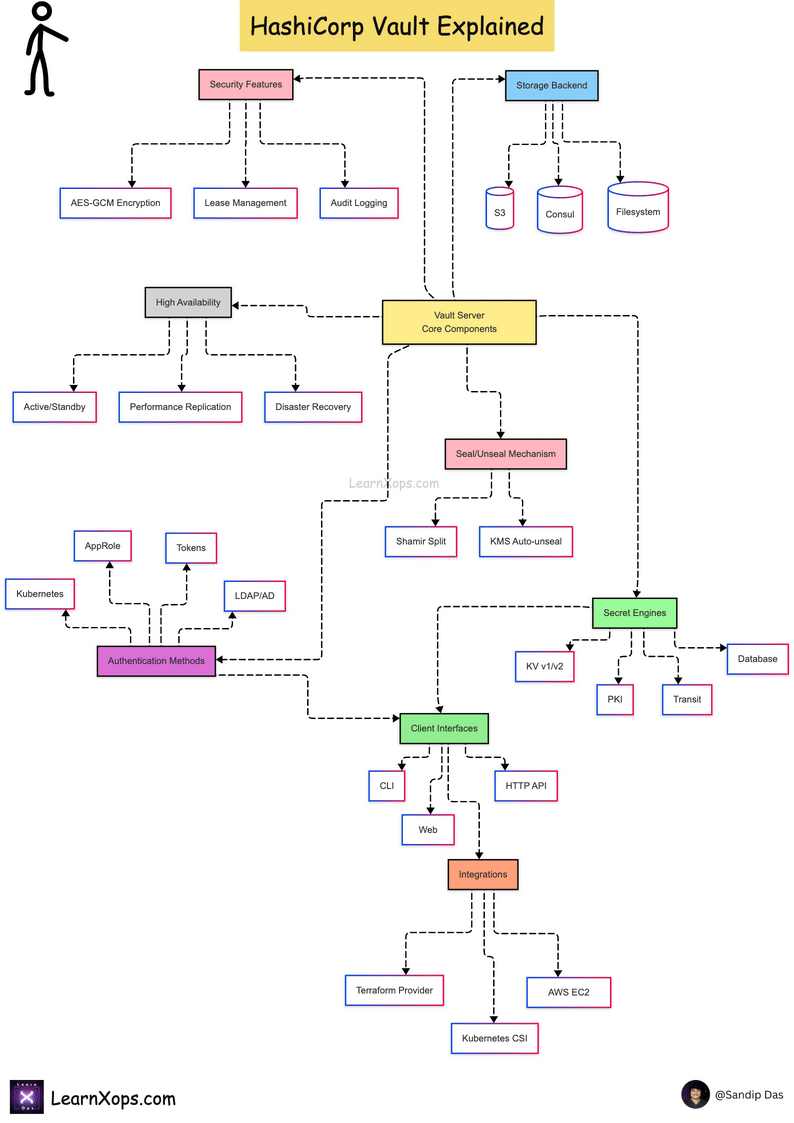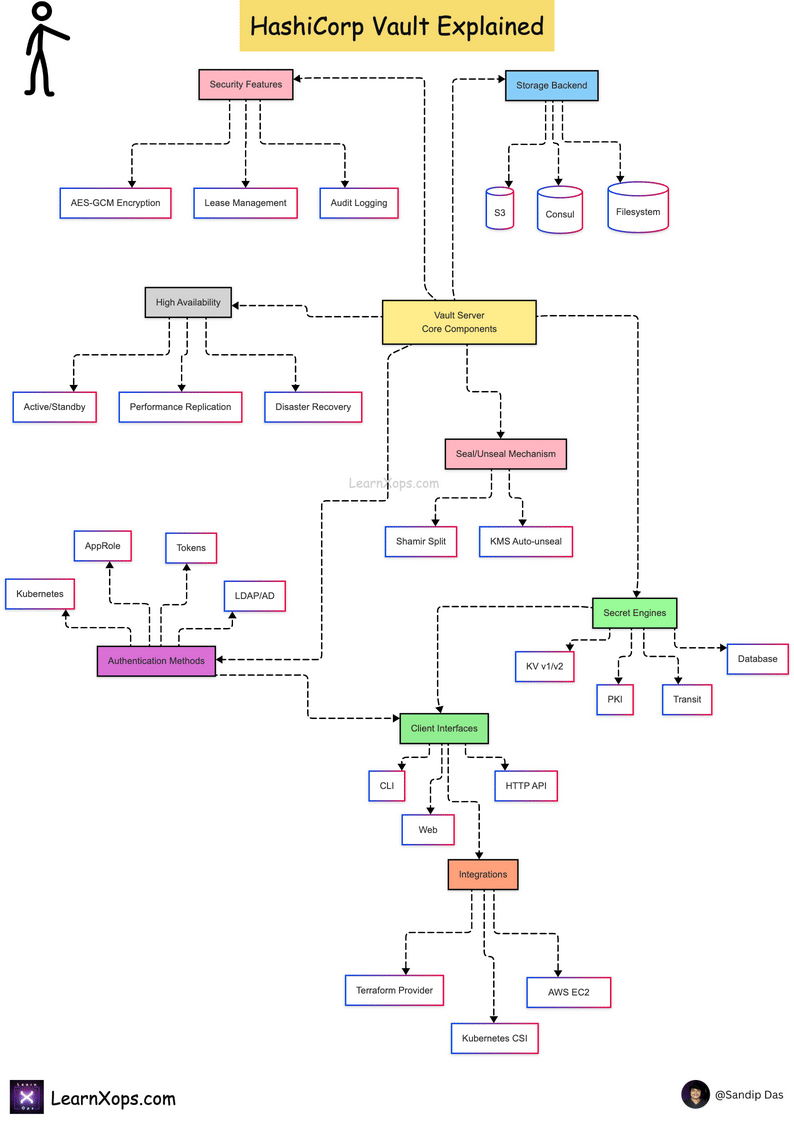
Download a high-resolution copy of this diagram here for future reference.
Read the full article on learnxops.com.
Topics: Hashicorp Vault, Secrets Management, Community, DevOps, News, 60 Days of DevOps